Authenticator Login Plus 1.0.3 Fixes OTP Enrollment and Multilingual 2FA Issues

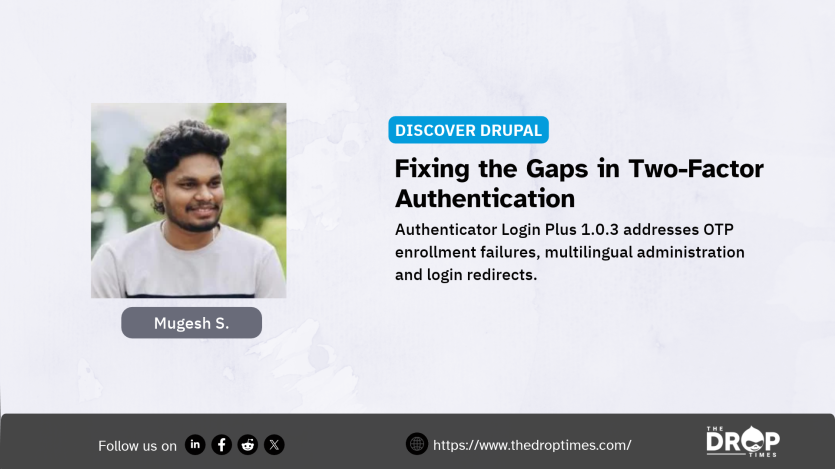
Authenticator Login Plus (2FA) 1.0.3, released on 11 November 2026, fixes three moderately critical authentication-bypass vulnerabilities and four additional problems involving one-time password (OTP) enrolment, multilingual administration, login redirects and QR-code dependencies. The Drupal module's maintainer, Mugesh S, announced the update, which the release notes urge all sites using the module to install.
The release changes how Drupal login flows enforce a second factor, including logins through one-time links, single sign-on modules and code that invokes user_login_finalize(). Such integrations now require the second factor before the account is fully logged in. The release notes also explain that operations performed by other modules after login finalisation, including ExternalAuthEvents::LOGIN, now occur only after the second-factor challenge has been completed.
Three Authentication-Bypass Advisories Addressed
The update fixes SA-CONTRIB-2026-320 (CVE-2026-126729), an authentication-bypass issue involving providers that authenticate on each request. The advisory describes a situation in which an attacker knowing an account's password could use its permissions without the second factor if a suitable per-request provider, such as HTTP Basic Authentication, and an alternative API authentication route were enabled.
SA-CONTRIB-2026-321 (CVE-2026-126730) concerns actions that could run before two-factor authentication finished. Someone possessing a first factor, such as a valid one-time login link, could trigger login-related actions, including updates to the account's last-login time and hooks implemented by other modules. The impact depends on which integrations respond to those hooks.
The third advisory, SA-CONTRIB-2026-322 (CVE-2026-126731), describes a timing-dependent weakness that could lead to account takeover or access to another account's two-factor setup under particular conditions. The advisory specifies that an attacker must already have an account, control the victim's email address or know the victim's password, and win a race condition. All three advisories rate the vulnerabilities as moderately critical and identify versions before 1.0.3 as affected.
The DropTimes previously covered the vulnerabilities in its 11 November Drupal contributed-project security roundup. The new release's implications extend beyond applying a patch: administrators should check whether custom or external authentication integrations assume that login hooks or events run before the second factor is entered.
OTP Enrolment and Administration Fixes
Version 1.0.3 also addresses a configuration problem in which changing the OTP code length or validity period could lock out users already enrolled with earlier settings. Issue #3634529 records the fix: the module now stores these values for each enrolment instead of relying solely on later site-wide settings. The release notes do not establish whether every account already affected by a previous change is automatically recovered; administrators should verify such accounts individually.
On multilingual Drupal sites, the 2FA administration overview previously displayed some users more than once. Issue #3634531 fixes the listing so that each user appears once. This was a duplicated display entry, not evidence that the system had created multiple user accounts.
Another correction, issue #3634534, removes a doubled base path in the Continue link after mandatory two-factor enrolment on websites installed in a subdirectory. Issue #3635043 adds compatibility with bacon/bacon-qr-code 3.x, allowing installations alongside endroid/qr-code 5.0.8 or later.
The release follows coordination involving module maintainer Mugesh S, Jürgen Haas, Juraj Nemec and other Drupal Security Team members, as acknowledged in the maintainer's release announcement. The security advisories identify Jürgen Haas and Mugesh S among the contributors who fixed the vulnerabilities.
Update and Test Authentication Integrations
The project page and version 1.0.3 release information list compatibility with Drupal 10, 11 and 12. Affected sites should update to 1.0.3, run database updates using drush updb or /update.php, and clear caches, as instructed in the release notes.
Administrators should then test ordinary 2FA login, one-time login links, single sign-on integrations, REST or JSON authentication flows where applicable, and mandatory enrolment. Those checks are especially important for custom integrations that rely on user_login_finalize() or post-login events, because completion of the second factor now changes when that code executes.
References
-
-
Authenticator Login Plus (2FA) - Moderately critical - Authentication bypass - SA-CONTRIB-2026-320 | Drupal.org, Drupal Security Team (11 November 2026)
-
Authenticator Login Plus (2FA) - Moderately critical - Authentication bypass - SA-CONTRIB-2026-321 | Drupal.org, Drupal Security Team (11 November 2026)
-
Authenticator Login Plus (2FA) - Moderately critical - Authentication bypass - SA-CONTRIB-2026-322 | Drupal.org, Drupal Security Team (11 November 2026)
ASK: Drupal Community Needs Your Support
View all →
Disclosure: This content is produced with the assistance of AI.
Note: The vision of this web portal is to help promote news and stories around the Drupal community and promote and celebrate the people and organizations in the community. We strive to create and distribute our content based on these content policy. If you see any omission/variation on this please reach out to us at #thedroptimes channel on Drupal Slack and we will try to address the issue as best we can.
Related People


You may also like