Drupal Core Security Update Fixes CKEditor XSS in Content Editing Workflow

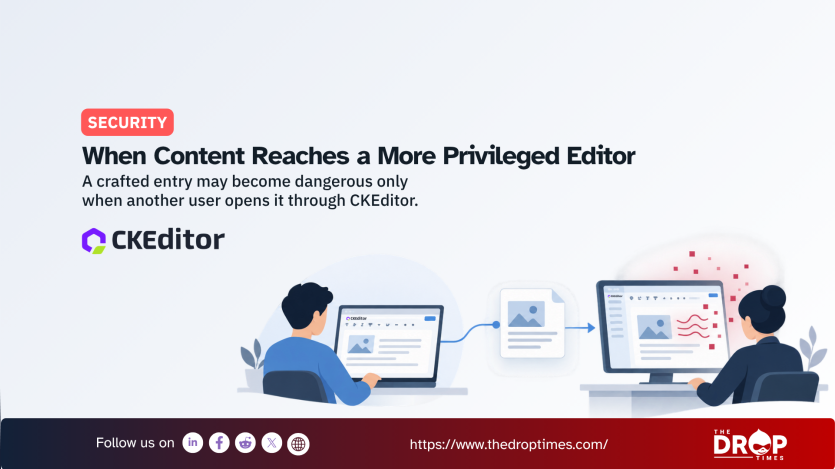
Supported Drupal 10 and Drupal 11 branches received security updates on 16 September 2026 to address a cross-site scripting (XSS) vulnerability in CKEditor 5. The SA-CORE-2026-013 advisory rates the issue Moderately critical at 13/25 and says a user who can create or edit content may be able to target users who later access that content through CKEditor, including site administrators. Drupal lists exploit availability as theoretical.
An attacker does not need permission to use CKEditor for the scenario Drupal describes. The relevant access requirement is the ability to create or edit content, which may then be processed by another user with access to the WYSIWYG editor. Drupal says the vulnerability is possible when a site is configured to use CKEditor for WYSIWYG editing.
Upstream, CKEditor's security advisory traces the flaw to prototype pollution in es-toolkit, a dependency used by the editor engine. According to CKEditor, a crafted style attribute value can lead to JavaScript execution when processed by the editor. The upstream project incorporated a fix after the underlying dependency was patched.
Drupal lists affected versions as >=10.5.0 <10.6.17, >=11.0.0 <11.3.17, and >=11.4.0 <11.4.7. Sites on supported branches should update to Drupal 10.6.17, 11.3.17, or 11.4.7 as appropriate. Drupal 10.5.x and below and Drupal 11.2.x and below are end-of-life and do not receive security coverage, so affected sites on those branches need to move to a supported release.
CKEditor also disclosed another XSS vulnerability in the same release cycle that Drupal says does not affect Drupal core but may affect custom plugins or other use cases. Drupal advises site owners to review contributed projects that may use additional CKEditor plugins not packaged with core. Sites should follow the remediation for their supported Drupal branch and review separately managed CKEditor extensions for upstream security updates.
ASK: Drupal Community Needs Your Support
View all →
Disclosure: This content is produced with the assistance of AI.
Note: The vision of this web portal is to help promote news and stories around the Drupal community and promote and celebrate the people and organizations in the community. We strive to create and distribute our content based on these content policy. If you see any omission/variation on this please reach out to us at #thedroptimes channel on Drupal Slack and we will try to address the issue as best we can.
You may also like