Two Guides Address Drupal Security and Decoupled CMS Reliability

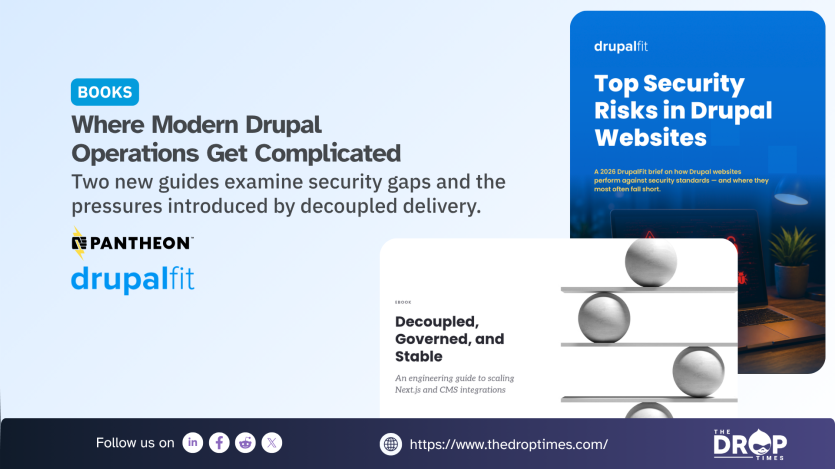
Two recent resources address different operational concerns for teams maintaining modern Drupal implementations. DrupalFit's Top Security Risks in Drupal Websites in 2026 focuses directly on Drupal security, while Pantheon's Decoupled, Governed, and Stable examines reliability and governance in decoupled Next.js and CMS deployments.
The DrupalFit resource is aimed at teams reviewing security risks around Drupal websites. Its scope is Drupal-specific, making it the more directly applicable of the two resources for maintainers assessing the security posture of an existing site.
Pantheon's guide focuses on the operating model behind decoupled implementations rather than a particular CMS. It identifies production problems including unreliable previews, stale content, caching inconsistencies and differences between environments, then looks at shared practices for preview, revalidation, releases, observability and recovery.
The Pantheon guide also introduces a five-level maturity model intended to help engineering and platform teams move from project-by-project fixes toward a repeatable approach across a larger site estate. Although the guide is not Drupal-specific, those concerns apply to organisations using Drupal as the content backend for a decoupled frontend.
The two resources therefore address different layers of operational risk. DrupalFit concentrates on the security of the Drupal site itself, while Pantheon focuses on the reliability and governance of the wider delivery architecture around a decoupled CMS.
ASK: Drupal Community Needs Your Support
View all →
Disclosure: This content is produced with the assistance of AI.
Note: The vision of this web portal is to help promote news and stories around the Drupal community and promote and celebrate the people and organizations in the community. We strive to create and distribute our content based on these content policy. If you see any omission/variation on this please reach out to us at #thedroptimes channel on Drupal Slack and we will try to address the issue as best we can.
Related Organizations
You may also like