Drupal Security Team Confirms Four Full-Member Promotions

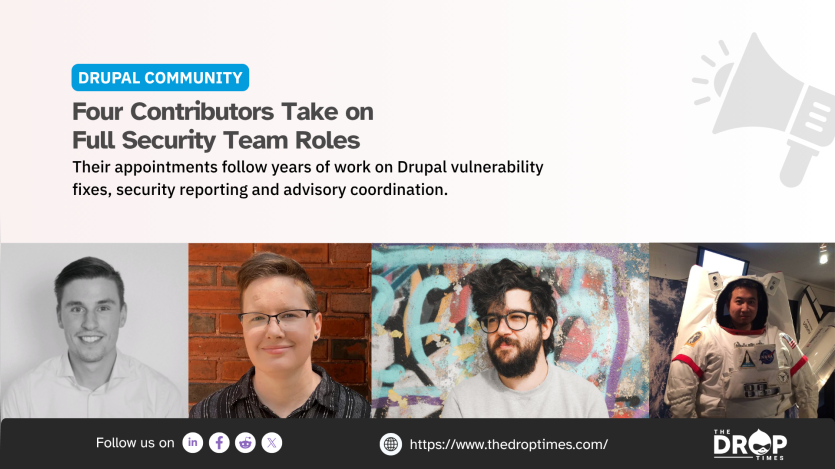
Following provisional service with the Drupal Security Team, Pierre Rudloff, Joseph Zhao, Bram Driesen and Swan Kalata have been welcomed as full members. Greg Knaddison announced the promotions on behalf of the team on 8 October 2026, noting that the post was published later than the membership changes themselves.
The announcement recognises four contributors whose public records already include reporting vulnerabilities, helping prepare fixes, coordinating advisories, contributing to Drupal core and supporting the wider community. The Security Team said each had demonstrated commitment, trustworthiness and effectiveness during provisional membership. Their individual histories also show how security-team participation can extend well beyond a single type of contribution.
Pierre Rudloff: Security Testing, Advisory Work and Reusable Guidance
Rudloff is a web developer at Insite in Lille, France. He has contributed to Drupal since 2019, and the Security Team credits him with more than 70 security advisory contributions.
His public contribution record includes work on the Security Review module, where fixes have addressed checks that could produce misleading security results under particular site configurations. He was also credited among the coordinators of SA-CORE-2026-001, involving an AJAX modal cross-site scripting issue, and SA-CORE-2026-004, a highly critical SQL injection vulnerability affecting Drupal sites using PostgreSQL.
Rudloff also created the Drupal Security Tips repository. The project documents recurring vulnerability patterns drawn from security advisories and the patches used to address them, turning experience from security response into reusable guidance for developers reviewing Drupal code.
Joseph Zhao: Reporting, Fixing and Mentoring Across the Ecosystem
Zhao is a solution architect and open-source developer based in Australia who has worked with open-source software since 2004. His Drupal contributions span patches, modules, themes, installation profiles, documentation, translations and automated tests. The Security Team also highlighted his work reviewing project applications and mentoring newer contributors.
His security record includes both reporting and fixing vulnerabilities. The March 2025 Formatter Suite advisory credits Zhao and Daniel Wehner with reporting a cross-site scripting issue caused by insufficient sanitisation of link attributes, with Zhao also among the contributors to the fix. Related advisories for Link Field Display Mode Formatter and RapiDoc OAS Field Formatter also credit him with reporting or fixing similar problems.
Zhao also contributed to SA-CORE-2025-004, which addressed insufficient sanitisation of Link field attributes in Drupal core. Those records identify him as a provisional Security Team member at the time, showing that his path to full membership already included work across both contributed projects and core.
Bram Driesen: Advisory Coordination and Community Leadership
Driesen is a Drupal developer at Sopra Steria in Belgium and has contributed to Drupal since 2015. His work combines development and security contributions with an active role in the Belgian and wider European Drupal community.
He participated in the same March 2025 link-attribute security response, with credits across contributed-project and Drupal core fixes. The December 2025 Tagify advisory later credited him with both fixing and coordinating a vulnerability involving insufficient sanitisation. At that point, he was still identified publicly as a provisional Security Team member.
Driesen's community work extends beyond security. He co-organises the Drupal User Group Belgium and has helped organise DrupalCamps in Antwerp, Ghent and Leuven as well as Drupal Dev Days Ghent. He also serves as Photography Lead for DrupalCon Europe.
Swan Kalata: Core Security and Long-Running Contribution
Kalata is an architect and technical lead at Tag1 Consulting in the United States. They have been active in the Drupal community for nearly 17 years and, according to the Security Team, have contribution credits on more than 180 issues, including nearly 70 involving Drupal core.
Their public security work includes fix credits on Drupal core advisories and later coordination responsibilities. Kalata contributed to SA-CORE-2025-006, which addressed a gadget chain that could be exploited together with a separate insecure deserialisation vulnerability. They were subsequently credited with coordinating significant core advisories, including the May 2026 PostgreSQL SQL injection issue and SA-CORE-2026-005, a critical PHP object injection vulnerability.
The Security Team's announcement also points to Kalata's work as a community mentor and participation in DrupalCon events internationally, adding long-running community involvement to their technical security record.
Shared Work Shows the Provisional Path in Practice
The four contributors have not worked in isolation. A 23 September 2026 advisory for Stop Administrator Login credits Rudloff as the reporter, Driesen among the fix contributors and Rudloff, Driesen and Kalata among the coordinators. The advisory provides a recent example of several of the new full members taking different roles in the same vulnerability response.
The Drupal Security Team's documented onboarding process describes provisional members taking part in multiple security issues before being reassessed for wider responsibilities. The public records of Rudloff, Zhao, Driesen and Kalata show experience across reporting, fixing and coordination, while the decision to grant full membership also depends on the team's internal assessment of trust and judgement.
The four join more than 20 volunteers currently listed on the Drupal Security Team. The 8 October announcement does not specify when each promotion formally took effect, so its significance is the public recognition of work that was already underway rather than the beginning of their security involvement.
ASK: Drupal Community Needs Your Support
View all →
Disclosure: This content is produced with the assistance of AI.
Note: The vision of this web portal is to help promote news and stories around the Drupal community and promote and celebrate the people and organizations in the community. We strive to create and distribute our content based on these content policy. If you see any omission/variation on this please reach out to us at #thedroptimes channel on Drupal Slack and we will try to address the issue as best we can.
Related People


You may also like